Retail · SaaS
A point-of-sale system that keeps sales, stock and receipts together on till, tablet and phone.
Screen capture, 1908 × 944
Your apps, APIs, networks and cloud attacked the way a real attacker would. Every finding proven, fixed and retested.
Six tests across every layer of your product, from the people who use it to the network it runs on.
Phishing and pretexting against the staff you choose, under rules agreed in writing.
Often found
Passwords typed into a fake sign-in, MFA prompts approved, details changed on a call.
Sign-in, sessions, access rules and every endpoint, attacked from outside and as a signed-in user.
Often found
Other users' data by changing an id, injection, broken sign-in, secrets in responses.
The iOS and Android app, the data it keeps on the phone and the API behind it.
Often found
Tokens stored in plain text, keys in the app bundle, an API that trusts the app.
The model's prompts, the data it can reach and the tools it can call.
Often found
Prompt injection, data leaking through answers, tools called for an attacker.
AI security testingIdentities, storage and exposed services in AWS, Azure or Google Cloud.
Often found
Public storage, roles with more access than they need, secrets in settings.
Internet-facing hosts and services, then the internal network from a foothold inside.
Often found
Open admin ports, out-of-date services, flat networks where one foothold reaches all.
How much the tester knows before starting: from nothing, like an outside attacker, to the code itself.
Tested from outside, knowing nothing.
Tested from inside an account, knowing some.
Tested with the code in hand, knowing everything.
Five steps, from the rules of the test to every fix retested. How long each takes depends on the scope; the estimate names the dates.
Targets, black, grey or white box, the test window and accounts, agreed in writing.
The attack surface mapped: every endpoint, role and exposed service, scanned first.
Findings exploited by hand and chained together, so each shows its real impact.
Every finding with its severity, proof and fix, walked through with your team.
The fixes tested again, with an updated report and a letter of attestation.
Three things at the end of a test, each in writing and each yours.
Every finding with its severity, the proof it can be exploited and how to fix it, and a summary for whoever signs off.
The team that found the issues fixes the ones you choose, then retests every fix and closes it in the report.
A letter saying what was tested and when, for the customers, partners or auditors who ask.
Custom software development across industries: web, mobile and AI applications, built and security-audited by one team.
We also build software for insurance (insurtech), government (govtech), energy and media. If your industry is not listed, we can still build for it.
One studio that attacks your software, proves what it finds, fixes it and shows the fixes hold.
Scanners clear the ground; each weakness is then exploited by hand, and the report shows the steps that did it.
The engineers who found the flaw fix it if you want, so nothing is lost handing the report to another team.
Each fix is attacked again the way the flaw was first exploited, then closed in the report or marked still open.
An attestation letter says what was tested and when, so you can show it without sharing the report.
Scope, rules of engagement, price and dates in writing after a first call, before any testing starts.
Signed before we see an account, a document or a line of code, and the report and its evidence are yours.
The tools a test runs on the way in, before the manual work that finds what they miss.
Three products of our own, built and tested to the same standard as the work we do for clients.
Retail · SaaS
A point-of-sale system that keeps sales, stock and receipts together on till, tablet and phone.
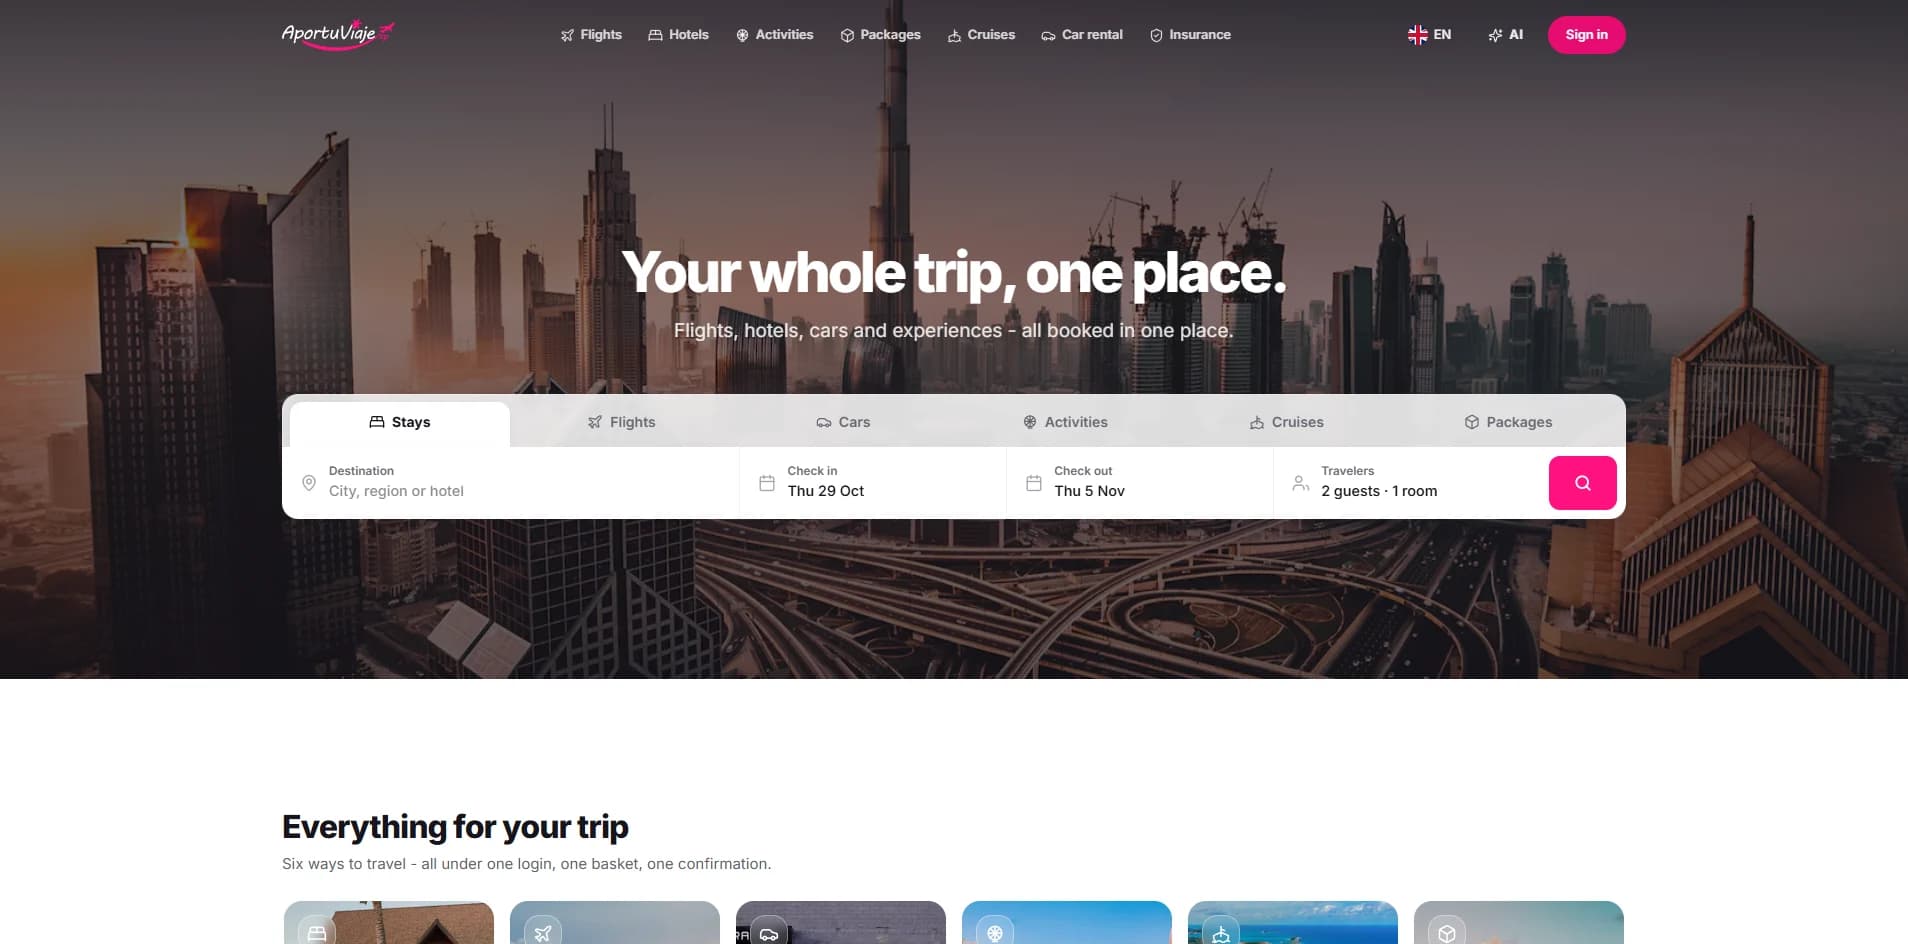
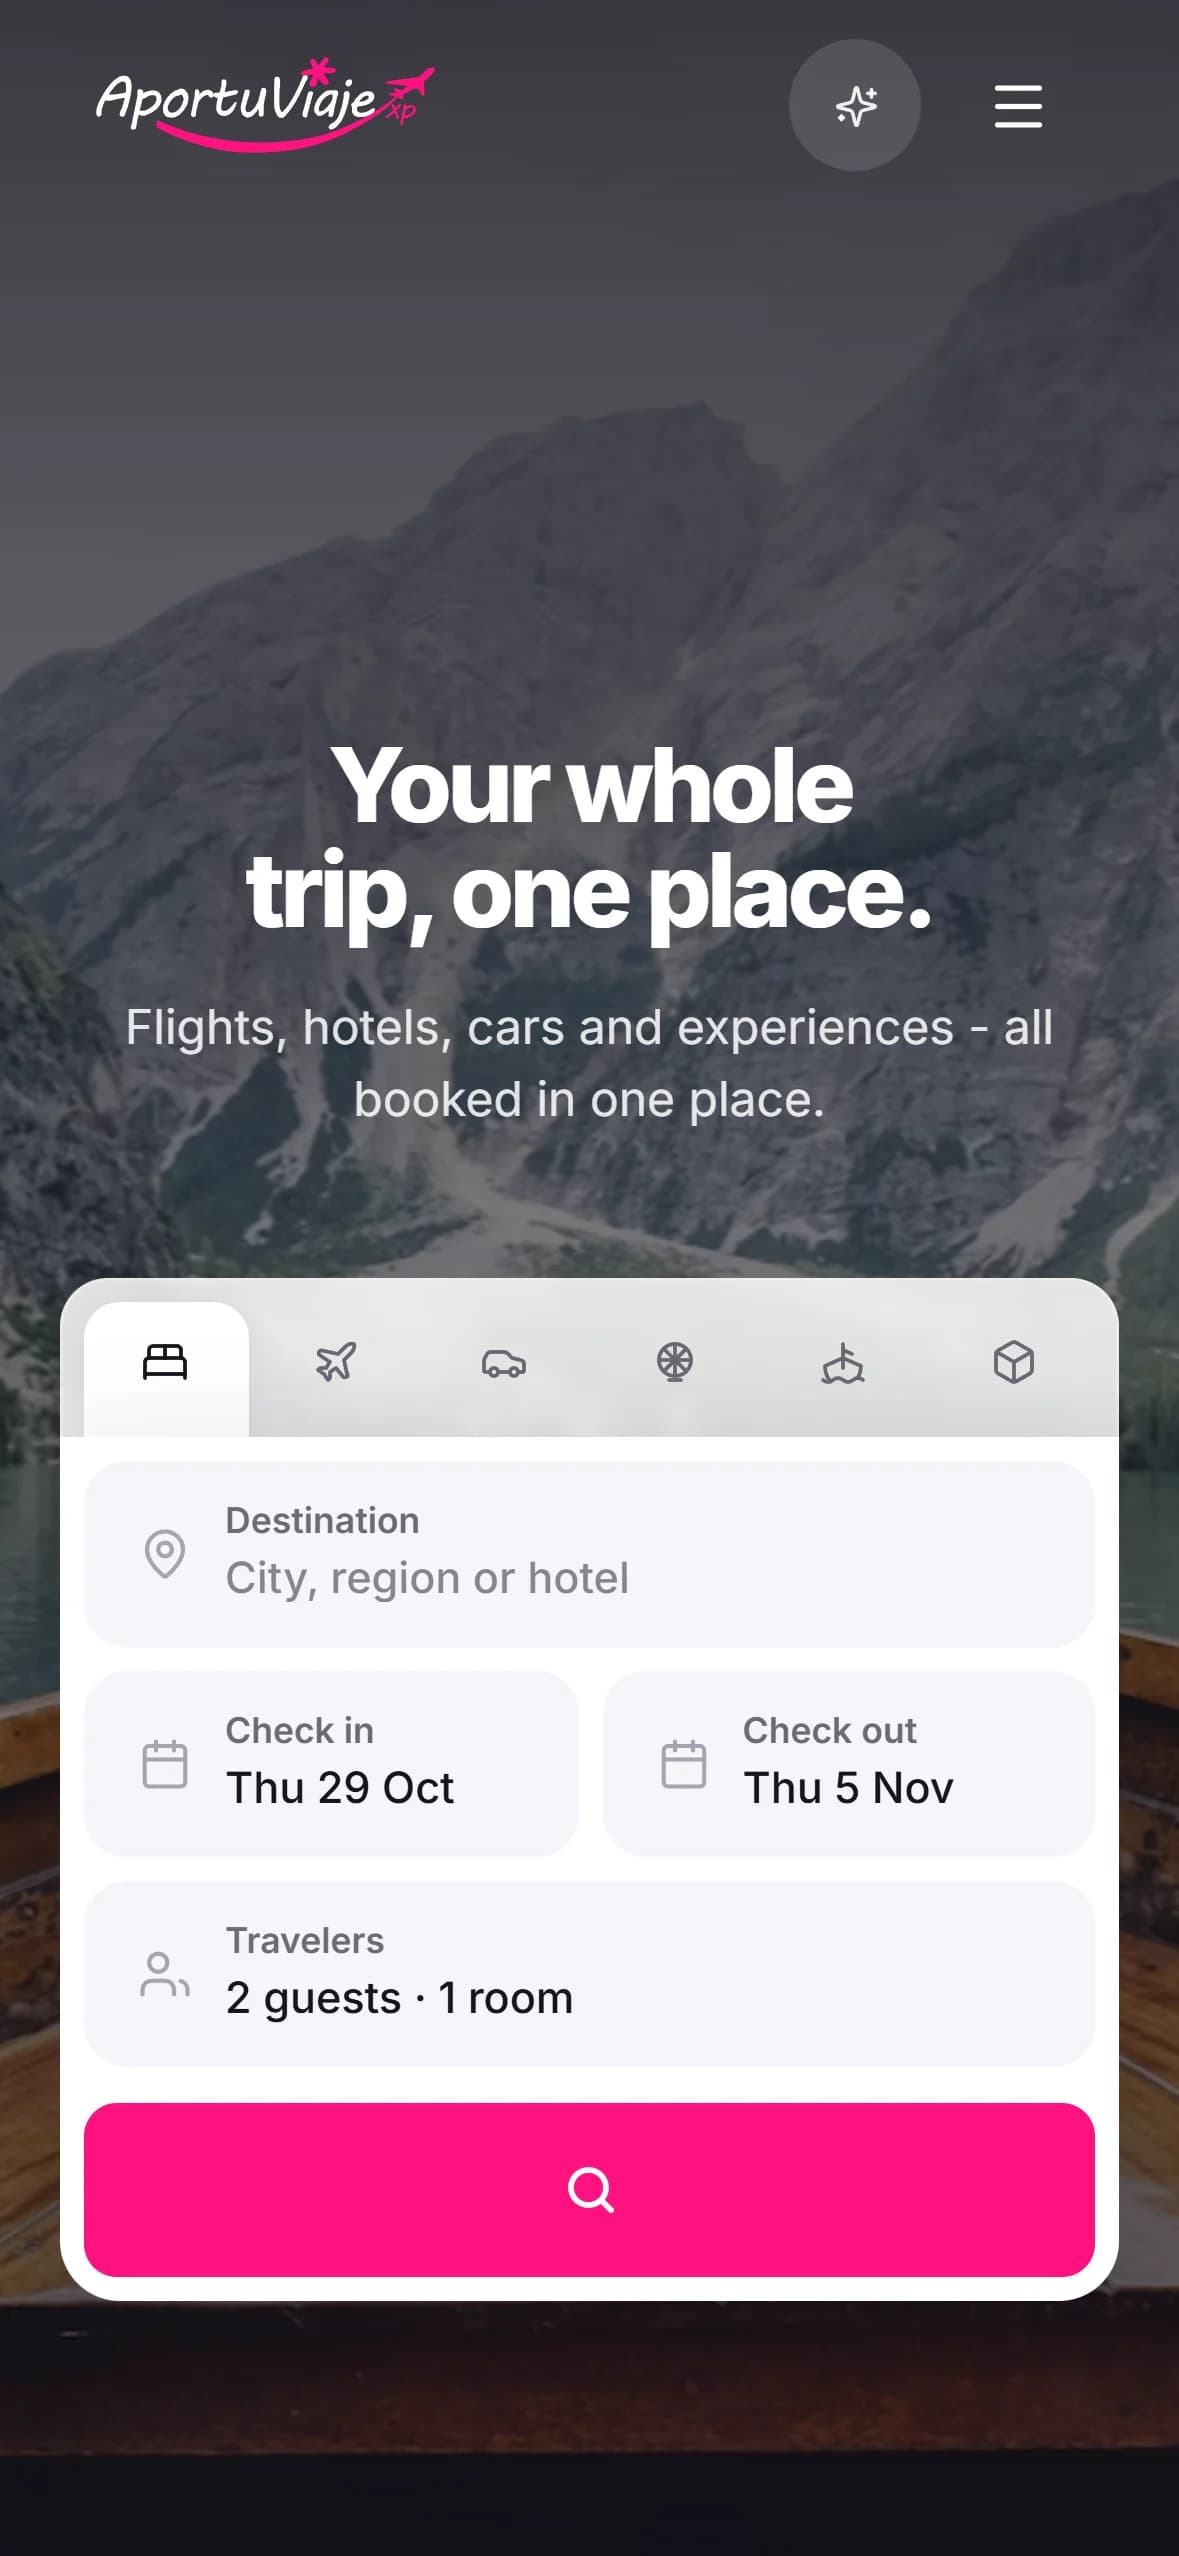
Travel
A travel booking app whose AI assistant finds flights, hotels and trip ideas, through to a confirmed booking.
AI
An AI assistant for customer support and sales that answers questions and guides buyers.
The ones teams ask before they book one, answered plainly.
It depends on what is in scope — one web app, a mobile app and its API, a network, a cloud account. After a first call you get a written estimate with the scope, the price and the dates, before any testing starts.
It depends on the scope: one API takes less time than an app, its API and the cloud behind it. The estimate names the dates, and the testing window is agreed before anything starts.
Black box starts where an outside attacker would, with no inside knowledge. Grey box starts with a user account and some documentation, like a signed-in customer. White box adds the code and the architecture, for the deepest coverage.
A security audit reads the code, the configuration and the design against a standard; a penetration test attacks the running system the way an attacker would. Many teams need both, and we do both.
Testing runs on staging where one exists, in a window agreed with you and under written rules of engagement. Anything that could touch production is agreed first, and nothing destructive runs without your sign-off.
Written permission and the scope, a contact during the testing window, and for grey or white box the accounts, documentation or code the test uses. An NDA is signed before any of it.
A report: every finding with its severity, the proof that it can be exploited and how to fix it, and a summary for the people who sign off. It is yours.
Yes. A retest checks each fix against its finding and closes it in the report, or tells you what is still open. If you want, the team that found the issues fixes them first.
Yes. After the test you can have an attestation letter that says what was tested and when, for customers, partners or auditors who ask.
Yes. We attack them the way a user could — prompt injection, data leaking through the model, tools it can be tricked into calling — alongside the app they sit in.